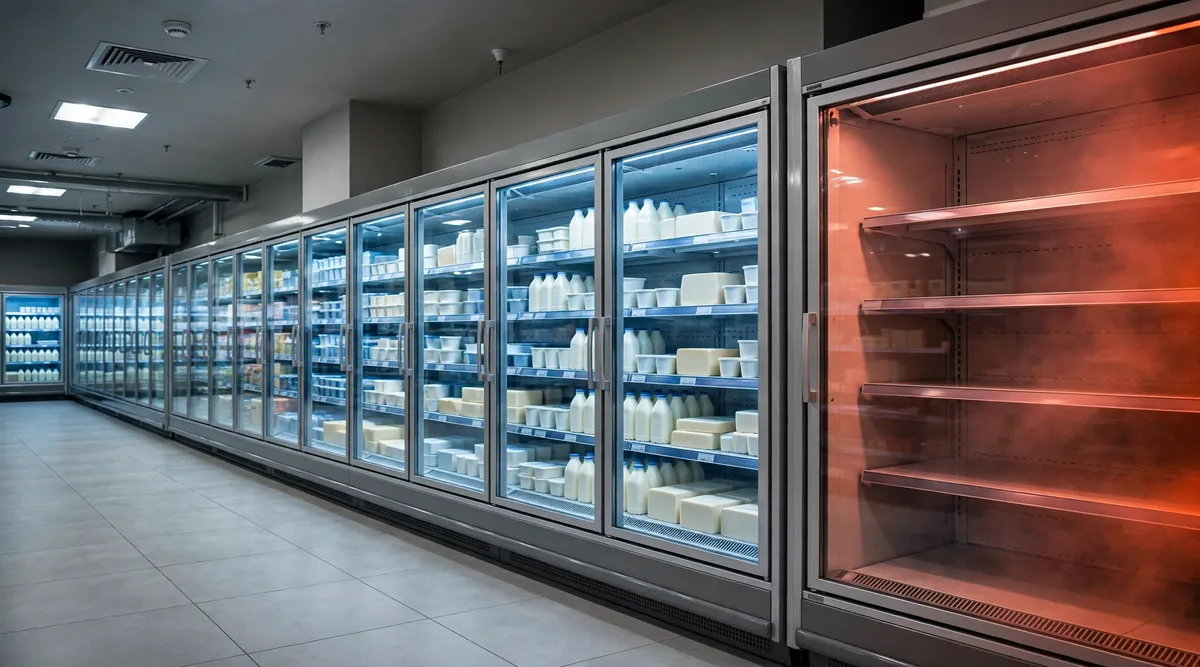
On the night of October 11–12, 2026, hundreds of French supermarkets woke up to a scene from a disaster film: display cases blowing warm air, meat and dairy ruined, frozen goods thawed, temperatures as high as 50°C. It was not a power failure. Attackers had seized the refrigeration management systems — Danish manufacturer Danfoss's controllers — and forced them into continuous defrost mode for hours, turning freezers into warming cabinets. Fires were reported. The Paris prosecutor's office opened an investigation into what it called a "large-scale" cyberattack, and Prime Minister Sébastien Lecornu tasked France's cybersecurity agency, ANSSI, with the technical inquiry.
This article reconstructs what is publicly known: the timeline, the attack chain and techniques, the vulnerabilities involved, the state of attribution, and what defenders and the industry are doing about it.
Timeline of events
- May 20, 2025 — CISA publishes an advisory on an authentication-bypass flaw in Danfoss AK-SM 800A supermarket refrigeration controllers.
- August 1, 2025 — Danfoss releases patched firmware (4.2 / 4.3.1) for the AK-SM 8xxA series.
- August 9, 2026 — Claroty's Team82 publishes "Freeze the Controller, Defrost the Food," detailing flaws in the Danfoss AK-SM 800A including a hidden code-of-the-day login mechanism that bypasses authentication. The researchers report finding thousands of publicly accessible management interfaces on the open internet.
- Night of October 11–12, 2026 — the attack. Refrigeration controllers at stores across France are forced into continuous defrost cycles for roughly six hours overnight; temperatures climb toward 50°C.
- October 12, morning — staff discover the damage. Intermarché and Coopérative U executives confirm the attack publicly; the Paris prosecutor's office opens an investigation citing food losses and fires; Prime Minister Lecornu directs ANSSI to investigate.
- October 12–13 — ANSSI begins its technical investigation and coordinates with European counterparts. Danfoss confirms the affected units were legacy or outdated-firmware systems. Retailers discard all affected stock and mobilize refrigeration specialists.
How the attack worked
Investigators have not published the exact intrusion path, but the reported facts outline a coherent attack chain against operational technology:
1. Reconnaissance — finding the controllers
Claroty's researchers had already demonstrated that thousands of Danfoss management interfaces were reachable from the open internet, and reporting suggests the attackers may have used the Shodan search engine to locate exposed devices. Some units are connected via 3G cards for remote monitoring, widening the exposure beyond corporate networks.
2. Initial access — old firmware, weak authentication
Danfoss confirmed that most compromised units were legacy AK-SM800 and AK-SC355 controllers that no longer receive security updates — some running software unsupported since 2021 — plus AK-SM800A units on outdated firmware. Publicly documented flaws in this platform include:
- CVE-2025-41450 — authentication bypass (CVSS 8.2), fixed in firmware 4.2
- CVE-2025-41451 — remote code execution after login (CVSS 8.7), fixed in 4.3.1
- CVE-2025-41452 — web server configuration injection after login (CVSS 6.8), fixed in 4.3.1
- A hidden code-of-the-day login mechanism bypassing standard authentication, described in Claroty's August 2026 research
Which specific flaw was exploited in October has not been established — that distinction matters, and investigators have not named one.
3. Execution — weaponizing a legitimate function
Once inside the administrative console, the attackers needed no malware. They issued valid maintenance commands: continuous defrost cycles and raised temperature setpoints. Defrost is a routine function that normally runs briefly overnight to clear frost — held on for six hours with heaters engaged, it cooked the inventory instead. As one analyst put it, the attackers simply turned routine maintenance against the operators.
4. Impact — physical destruction at scale
Roughly 500 of France's ~15,000 stores were affected: around 300 Intermarché/Netto outlets, nearly 100 Coopérative U stores, 80 Carrefour supermarkets, about 5% of Monoprix locations, plus disruptions at E.Leclerc and Auchan. All affected food was discarded. Individual store write-offs are described at €50,000–€200,000 per site, with industry-wide damage estimated in the tens of millions of euros. Fires broke out where equipment overheated. Sekoia's threat intelligence notes that Spain, Portugal, Poland, Germany, and Belgium were also affected; Dutch operator Ahold Delhaize reported a separate security issue the same weekend, though no connection has been confirmed.
Technique mapping (analyst assessment)
The following maps reported behaviors to MITRE ATT&CK for ICS. This is analytic assessment, not an official mapping — no authority has published one.
- T1595.002 — Vulnerability Scanning (Enterprise) / internet-wide scanning for exposed Danfoss management interfaces, consistent with Shodan-indexed controllers.
- T1190 — Exploit Public-Facing Application — the AK-SM web interfaces carrying CVE-2025-41450/41451/41452.
- T0855 — Unauthorized Command Message (ICS) — forged or abused legitimate defrost/setpoint commands sent to controllers.
- T0836 — Modify Parameter (ICS) — temperature setpoints driven to destructive values.
- T0816 — Device Restart/Shutdown (ICS, partial fit) — sustained abuse of the defrost function as a destructive control action.
The notable tradecraft point: this is a living-off-the-OT-land attack. No custom malware was needed because the controllers' own legitimate functions were the weapon.
Attribution: who did it
Honest answer: nobody knows publicly. As of this writing, no group has claimed responsibility, no ransom demand has been reported, no government has attributed the attack, and no indicators of compromise have been published. The absence of a claim is itself notable — documented pro-Russia hacktivist OT operations are typically claimed loudly on Telegram, and none of the usual ecosystems (or Iran's CyberAv3ngers-style actors) have surfaced here.
What can be said: the motive was destruction, not profit — no encryption, no data theft, no extortion. Analysts have speculated about state or hybrid-warfare actors given the sabotage profile and the targeting of food supply, and the incident lands weeks after President Macron ordered measures to protect French critical infrastructure from Russian hybrid activity. But speculation is not attribution, and any claim that surfaces later should be treated skeptically until corroborated with technical evidence.
IoCs: what is (and isn't) available
No IoCs have been published. No IPs, domains, hashes, or controller log excerpts have been released by ANSSI, Danfoss, or any vendor as of this writing. Rather than wait, defenders with similar estates can hunt the exposure that made this possible:
- Shodan:
http.title:"Danfoss"— baseline of indexed Danfoss management interfaces; addcountry:"CA"(or your country) to scope it home. - Firmware inventory: enumerate every Danfoss AK-SM800, AK-SC355, and AK-SM800A in your estate; anything end-of-life or below firmware 4.3.1 is in the same posture as the compromised French units.
- Network posture: identify controllers reachable from the internet or via cellular/3G paths that bypass corporate network controls — these were the soft entry points.
- Controller logs: review administrative-console access logs for logins outside maintenance windows and any defrost or setpoint changes not tied to a work order.
Remediation and response
Retailers: discarded all affected perishable stock to eliminate health risk; mobilized refrigeration specialists to restore cooling; convened crisis meetings with maintenance firms and Danfoss; several chains kept affected display units out of service while assessing damage. Intermarché has warned its insurance may not cover this class of damage — expect contested liability.
French authorities: the Paris prosecutor's anti-cybercrime unit is leading the criminal investigation, with victim counting and damage assessment underway; ANSSI is conducting the technical investigation and coordinating with European counterparts since other countries may be affected; the prime minister's office is assessing whether other French firms are at risk.
Danfoss: confirmed the incidents, identified legacy end-of-life equipment and outdated firmware as the common factors, reiterated long-standing advice to upgrade or replace AK-SM800/AK-SC355 units and patch supported systems, and is collaborating with affected customers. Note the regulatory backdrop: the EU Cyber Resilience Act's 24-hour reporting duty for actively exploited vulnerabilities has applied to vendors since September 2026.
Structural fixes defenders should take away: segment OT management interfaces off the internet entirely; inventory end-of-life controllers the same way you inventory end-of-life software — they are unpatchable by definition; treat vendor remote-monitoring paths (including cellular) as part of the attack surface; and monitor controller command logs for out-of-window administrative actions, because the next attack may again use nothing but legitimate commands.
Sources
- BBC News via WebProNews — store counts and Coopérative U statement
- TBS News — prosecutor's office, ANSSI tasking, Sekoia's multi-country assessment
- Security Affairs — Danfoss statement, Claroty research context, investigation details
- IT Security Guru — legacy controller details, Shodan exposure reporting
- Cellcog.ai — CVE table for the AK-SM 8xxA series and Claroty timeline
- Cold Chain Under Fire (Substack) — attribution status and governance analysis