Incident response · Threat intelligence · SOC leadership
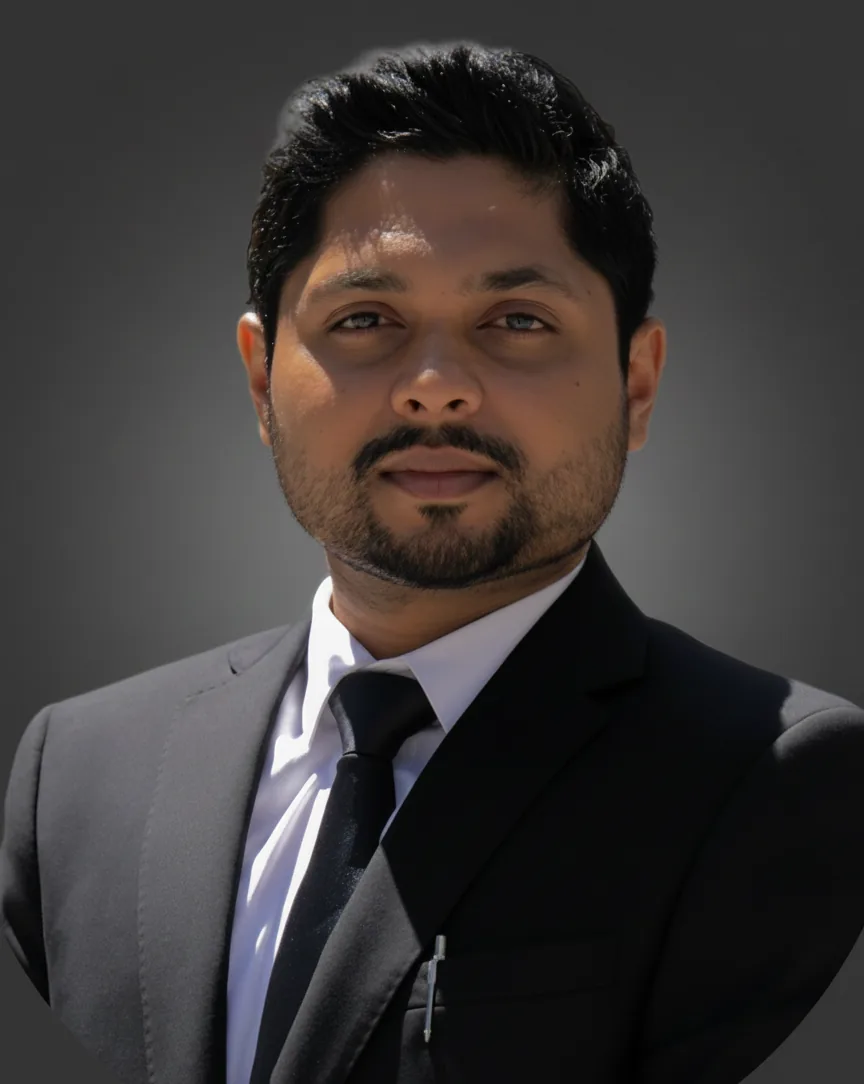
Amit Vijayan.
I turn complex security incidents into clear, repeatable action.
Product Security Incident Response Specialist at Ericsson, with 8+ years across Morgan Stanley, Microsoft, PwC and Paysafe — connecting technical evidence, decisive response and stronger detection.
Explore
Go deeper.
Investigation write-ups, detection playbooks and a daily threat brief — all written from real incident-response work.
Articles
Threat Hunting Playbooks
Hands-on investigation write-ups, detection engineering notes and playbooks you can apply in your own SOC.
Browse playbooks Daily briefCyber News
The day’s breaches, ransomware and vulnerabilities — a concise threat brief updated every morning.
Read today’s brief Free · alwaysMentoring
Guidance for fresh graduates breaking into cybersecurity — resume reviews, interview prep and career advice.
Request mentoringLatest work
Still shipping.
New investigations and threat briefs, published on a steady cadence — most recent first.
Threat Hunting Playbooks
Hunting Rogue OAuth Consent Grants in Entra ID
The user did everything right — spotted the phish, kept MFA intact. Then they clicked “Accept”.
Cyber News
Daily Cyber Threat Brief — October 10, 2026: Chaos Ransomware Claims 1.5 TB of Astrana Health Data
The Chaos group claims 1.5 TB of exfiltrated patient data — plus today’s other breaches, advisories and threat-actor moves.
Technical expertise
From signal to response.
Hands-on experience across the systems, evidence and operational practices that make investigations defensible and response repeatable.
SIEM & Security Analytics
 Splunk ES
 SentinelArArcSight
 LogRhythm
 Elastic
 QRadar
Endpoint Detection & Response
 CrowdStrike
 Cortex XDRCbCarbon Black
 SentinelOne
 Trellix
 Microsoft Defender
Digital Forensics
 Volatility
 Autopsy
 WiresharkFlFLARE VM
 CyberChef
 EnCase
Threat Intelligence & Hunting
 MITRE ATT&CK
 MISPTcThreatConnect
 Maltego
 Shodan
 Recorded Future
Incident Response
RpResponse playbooksIrInsider riskBcBreach coordinationSaAutomation
Certification Background
 eJPT
 CEH v11SC-100SC-200SC-900AZ-500AZ-900
Professional journey
Built in the work.
Progressing from frontline security operations to incident-response leadership across telecommunications, financial services, technology and consulting.
Product Security Incident Response Specialist
- Product security incident response at Ericsson — triage, coordination and remediation follow-through for security issues affecting Ericsson products.
- Working with product and engineering teams on vulnerability response and security advisories.

Director — Incident Response & Operations
- Led incident response and recovery for 50+ high-severity events a year; insider-risk playbooks built with HR and legal cut escalation delays 40%.
- Built AI copilot agents for SOC workflows and expanded insider-threat monitoring coverage 35%.
- Coordinated PIPEDA/GDPR breach notifications for 20+ incidents at 100% compliance; ran vendor-breach response across 20+ vendors.
Business Program Manager — Incident Response & Detection
- Shipped 30+ new detection scenarios across 5+ business areas; authored 20+ detection engineering playbooks and runbooks.
- Wrote 30+ threat-intelligence advisories and delivered Nation State Notifications to 100+ clients during DART engagements.
- Trained a 34-member vendor team, cutting alert investigation time 30%.

Senior Associate — Cyber Security & Privacy
- Tuned 30+ monitoring use cases to cut false positives 45%, triaging 200+ alerts a month across 8+ client environments.
- Led 10+ incident-response workstreams and threat-intel initiatives, lifting response efficiency 35%.
- Authored 25+ playbooks and SOPs; trained 30 L1 analysts, improving ticket resolution 50%.
Security Operations Analyst
- Managed IAM across 25+ critical systems through 4 annual audits at 100% SOC1/SOC2 and PCI-DSS compliance.
- Triaged DLP and antivirus alerts daily; strengthened phishing awareness and incident-ticket workflows.
Background
Study. Prove. Contribute.
Formal security engineering education, continued certification work and community service beyond the day job.
Concordia University
Master of Information Systems Security Engineering

Rayat and Bahra University
Bachelor of Computer Science Engineering
7 certification tracks
eJPTCEH v11SC-100SC-200SC-900AZ-500AZ-900
OSINT for good
Volunteer analyst supporting TraceLabs and Innocent Lives Foundation investigations, alongside community service with Rotary Blood Bank and World Sikh Organization.
Let’s connect
Clear thinking.
Stronger defense.
Open to conversations about incident response, detection engineering and security operations.